Loading...
Searching...
No Matches
audit_log_cipher.h File Reference
At-rest encryption for ATNA audit log records (ISO 27799 compliance) More...
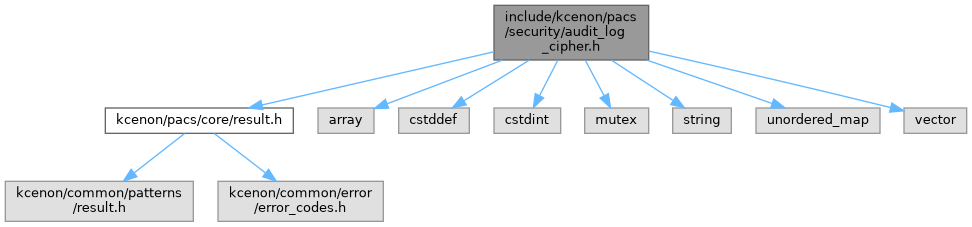
#include "kcenon/pacs/core/result.h"#include <array>#include <cstddef>#include <cstdint>#include <mutex>#include <string>#include <unordered_map>#include <vector>
Include dependency graph for audit_log_cipher.h:
This graph shows which files directly or indirectly include this file:
Go to the source code of this file.
Classes | |
| struct | kcenon::pacs::security::audit_cipher_key |
| A versioned symmetric key pair (data encryption + MAC) More... | |
| class | kcenon::pacs::security::audit_key_manager |
| Holds the active encryption key and any retired keys for decryption of historical records. More... | |
| class | kcenon::pacs::security::audit_log_cipher |
| Encrypts and decrypts single audit log records. More... | |
Namespaces | |
| namespace | kcenon |
| namespace | kcenon::pacs |
| namespace | kcenon::pacs::security |
| namespace | kcenon::pacs::security::detail |
Functions | |
| std::string | kcenon::pacs::security::detail::base64_encode (const std::uint8_t *data, std::size_t size) |
| Standard base64 encode (no line breaks) | |
| bool | kcenon::pacs::security::detail::base64_decode (const std::string &in, std::vector< std::uint8_t > &out) |
| Standard base64 decode; returns false on malformed input. | |
| bool | kcenon::pacs::security::detail::hex_decode (const std::string &in, std::uint8_t *out, std::size_t out_size) |
| Hex decode (lowercase or uppercase); returns false on malformed input. | |
| bool | kcenon::pacs::security::detail::constant_time_equal (const std::uint8_t *a, const std::uint8_t *b, std::size_t n) noexcept |
| Constant-time equality on byte buffers of equal length. | |
Variables | |
| constexpr const char * | kcenon::pacs::security::audit_cipher_format_tag = "PACSAUDIT" |
| Format version string embedded in every encrypted record. | |
| constexpr const char * | kcenon::pacs::security::audit_cipher_format_version = "v1" |
| constexpr std::size_t | kcenon::pacs::security::audit_cipher_key_bytes = 32 |
| AES-256 key length in bytes. | |
| constexpr std::size_t | kcenon::pacs::security::audit_cipher_mac_key_bytes = 32 |
| HMAC-SHA256 key length in bytes (equal to block size for full strength) | |
| constexpr std::size_t | kcenon::pacs::security::audit_cipher_iv_bytes = 12 |
| GCM IV length in bytes (NIST SP 800-38D recommended 96 bits) | |
| constexpr std::size_t | kcenon::pacs::security::audit_cipher_tag_bytes = 16 |
| GCM authentication tag length in bytes. | |
Detailed Description
At-rest encryption for ATNA audit log records (ISO 27799 compliance)
Provides AES-256-GCM authenticated encryption with HMAC-SHA256 integrity signing for audit log records. Supports key rotation by embedding a key identifier in every record so that historical records remain decryptable after rotation.
Record format (ASCII, single line, terminated by '
'):
*   PACSAUDIT|v1|<key_id>|<iv_b64>|<ciphertext_b64>|<tag_b64>|<hmac_b64>
*
Where:
- v1 is the format version tag
- key_id is the identifier of the key used to encrypt the record
- iv_b64 is the 96-bit AES-GCM initialisation vector (base64)
- ciphertext_b64 is the AES-256-GCM ciphertext (base64)
- tag_b64 is the 128-bit AES-GCM authentication tag (base64)
- hmac_b64 is an HMAC-SHA256 over the preceding fields (base64), bound to a separate MAC key for defence-in-depth per ISO 27799 §7.9
- See also
- ISO 27799:2016 §7.9 — Audit logging (integrity & confidentiality)
- HIPAA §164.312(b) — Audit controls
- Issue #1102
- Since
- 1.0.0
Definition in file audit_log_cipher.h.
