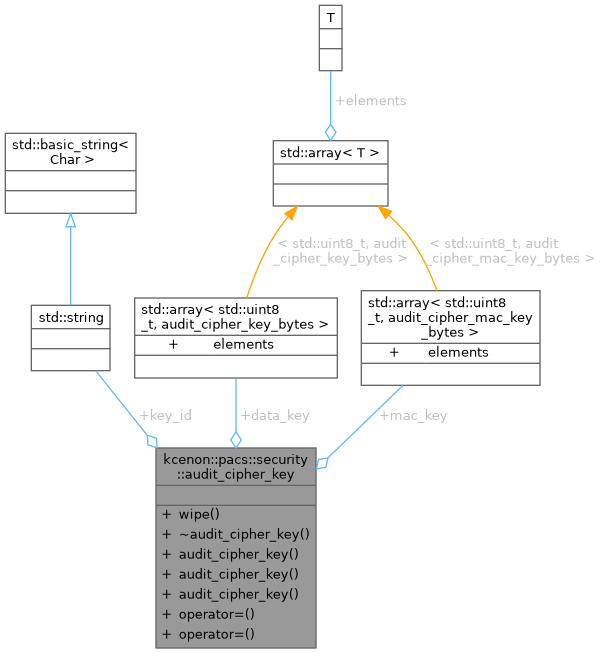
A versioned symmetric key pair (data encryption + MAC) More...
#include <audit_log_cipher.h>
Public Member Functions | |
| void | wipe () noexcept |
| Secure zero helper (wipes key material on destruction) | |
| ~audit_cipher_key () | |
| audit_cipher_key ()=default | |
| audit_cipher_key (const audit_cipher_key &)=default | |
| audit_cipher_key (audit_cipher_key &&) noexcept=default | |
| audit_cipher_key & | operator= (const audit_cipher_key &)=default |
| audit_cipher_key & | operator= (audit_cipher_key &&) noexcept=default |
Public Attributes | |
| std::string | key_id |
| Stable identifier (ASCII, non-empty, no '|' character) | |
| std::array< std::uint8_t, audit_cipher_key_bytes > | data_key {} |
| 256-bit AES data encryption key | |
| std::array< std::uint8_t, audit_cipher_mac_key_bytes > | mac_key {} |
| 256-bit HMAC-SHA256 key | |
Detailed Description
A versioned symmetric key pair (data encryption + MAC)
The encryption key is used for AES-256-GCM confidentiality; the separate MAC key provides an independent integrity check so that a compromise of the GCM tag alone does not imply forgery of records in storage.
Definition at line 81 of file audit_log_cipher.h.
Constructor & Destructor Documentation
◆ ~audit_cipher_key()
| kcenon::pacs::security::audit_cipher_key::~audit_cipher_key | ( | ) |
Definition at line 169 of file audit_log_cipher.cpp.
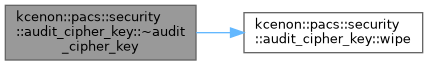
References wipe().
◆ audit_cipher_key() [1/3]
|
default |
◆ audit_cipher_key() [2/3]
|
default |
◆ audit_cipher_key() [3/3]
|
defaultnoexcept |
Member Function Documentation
◆ operator=() [1/2]
|
defaultnoexcept |
◆ operator=() [2/2]
|
default |
◆ wipe()
|
noexcept |
Secure zero helper (wipes key material on destruction)
Definition at line 161 of file audit_log_cipher.cpp.
References data_key, and mac_key.
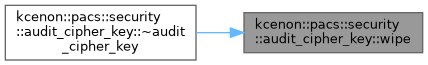
Referenced by ~audit_cipher_key().
Member Data Documentation
◆ data_key
| std::array<std::uint8_t, audit_cipher_key_bytes> kcenon::pacs::security::audit_cipher_key::data_key {} |
256-bit AES data encryption key
Definition at line 86 of file audit_log_cipher.h.
Referenced by kcenon::pacs::security::audit_key_manager::load_from_env(), and wipe().
◆ key_id
| std::string kcenon::pacs::security::audit_cipher_key::key_id |
Stable identifier (ASCII, non-empty, no '|' character)
Definition at line 83 of file audit_log_cipher.h.
Referenced by kcenon::pacs::security::audit_key_manager::load_from_env(), and kcenon::pacs::security::audit_key_manager::register_key().
◆ mac_key
| std::array<std::uint8_t, audit_cipher_mac_key_bytes> kcenon::pacs::security::audit_cipher_key::mac_key {} |
256-bit HMAC-SHA256 key
Definition at line 89 of file audit_log_cipher.h.
Referenced by kcenon::pacs::security::audit_key_manager::load_from_env(), and wipe().
The documentation for this struct was generated from the following files:
- include/kcenon/pacs/security/audit_log_cipher.h
- src/security/audit_log_cipher.cpp