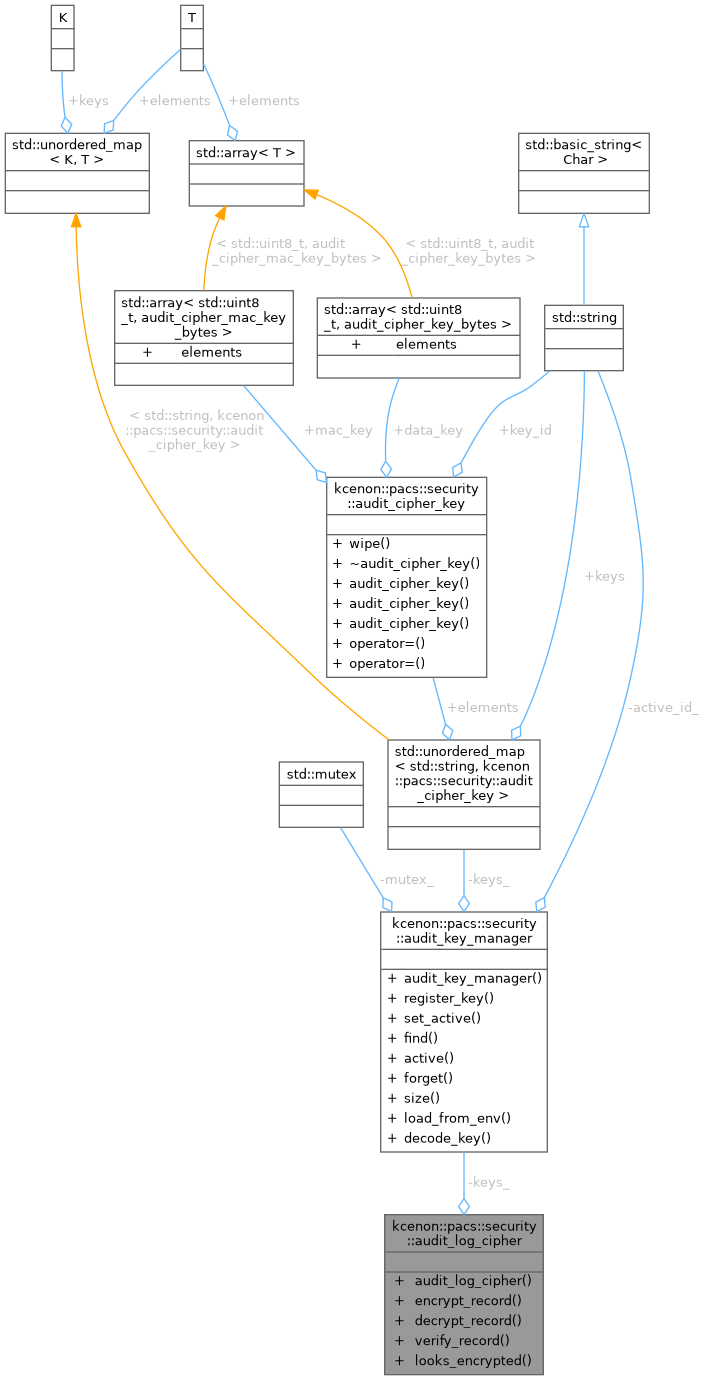
Encrypts and decrypts single audit log records. More...
#include <audit_log_cipher.h>
Public Member Functions | |
| audit_log_cipher (audit_key_manager &keys) | |
| Construct a cipher backed by the given key manager. | |
| Result< std::string > | encrypt_record (const std::string &plaintext) const |
| Encrypt a plaintext audit record. | |
| Result< std::string > | decrypt_record (const std::string &encoded) const |
| Decrypt a previously encoded record. | |
| VoidResult | verify_record (const std::string &encoded) const |
| Verify a record's authenticity without returning plaintext. | |
Static Public Member Functions | |
| static bool | looks_encrypted (const std::string &line) noexcept |
| Check whether a line appears to be an encrypted audit record. | |
Private Attributes | |
| audit_key_manager & | keys_ |
Detailed Description
Encrypts and decrypts single audit log records.
Instances are stateless with respect to plaintext content; they hold a reference to a key manager and generate a fresh random IV per record.
Thread-safety: all public methods are safe to call from multiple threads provided the referenced audit_key_manager outlives the cipher.
Definition at line 196 of file audit_log_cipher.h.
Constructor & Destructor Documentation
◆ audit_log_cipher()
|
explicit |
Construct a cipher backed by the given key manager.
- Parameters
-
keys key store (must outlive this cipher)
Definition at line 349 of file audit_log_cipher.cpp.
Member Function Documentation
◆ decrypt_record()
|
nodiscard |
Decrypt a previously encoded record.
Looks up the key by the embedded key_id. If the key is unknown, returns an error. If either the HMAC or the GCM tag fails to verify, returns a distinct integrity error (never a partial plaintext).
- Parameters
-
encoded single-line record produced by encrypt_record(trailing '
' is tolerated)
- Returns
- plaintext on success
Definition at line 658 of file audit_log_cipher.cpp.
References kcenon::pacs::pacs_error().
◆ encrypt_record()
|
nodiscard |
Encrypt a plaintext audit record.
Uses the currently-active key. A fresh 96-bit IV is drawn for every call from the OS CSPRNG. The returned string is the single-line serialised record (without trailing newline).
- Parameters
-
plaintext arbitrary byte string (typically an RFC 3881 XML audit message)
- Returns
- encoded record or an error if no active key is configured or the underlying crypto provider fails
Definition at line 650 of file audit_log_cipher.cpp.
References kcenon::pacs::pacs_error().
◆ looks_encrypted()
|
staticnodiscardnoexcept |
Check whether a line appears to be an encrypted audit record.
Definition at line 351 of file audit_log_cipher.cpp.
References kcenon::pacs::security::audit_cipher_format_tag, and kcenon::pacs::security::audit_cipher_format_version.
◆ verify_record()
|
nodiscard |
Verify a record's authenticity without returning plaintext.
- Returns
- VoidResult::ok if both HMAC and GCM tag verify, error otherwise
Definition at line 666 of file audit_log_cipher.cpp.
References kcenon::pacs::pacs_void_error().
Member Data Documentation
◆ keys_
|
private |
Definition at line 243 of file audit_log_cipher.h.
The documentation for this class was generated from the following files:
- include/kcenon/pacs/security/audit_log_cipher.h
- src/security/audit_log_cipher.cpp