Holds the active encryption key and any retired keys for decryption of historical records. More...
#include <audit_log_cipher.h>
Public Member Functions | |
| audit_key_manager ()=default | |
| void | register_key (audit_cipher_key key) |
| Register a key (idempotent by key_id; overwrites existing entry) | |
| VoidResult | set_active (const std::string &key_id) |
| Mark a previously-registered key as the active write key. | |
| const audit_cipher_key * | find (const std::string &key_id) const |
| Look up a key by identifier (returns nullptr if unknown) | |
| Result< audit_cipher_key > | active () const |
| Retrieve the active write key (error if none configured) | |
| void | forget (const std::string &key_id) |
| Drop a key by id (does nothing if it was not registered) | |
| std::size_t | size () const |
| Number of registered keys. | |
| VoidResult | load_from_env () |
| Load keys from environment variables. | |
Static Public Member Functions | |
| static VoidResult | decode_key (const std::string &encoded, std::uint8_t *out, std::size_t out_size) |
| Decode a hex or base64 key string into a fixed-size buffer. | |
Private Attributes | |
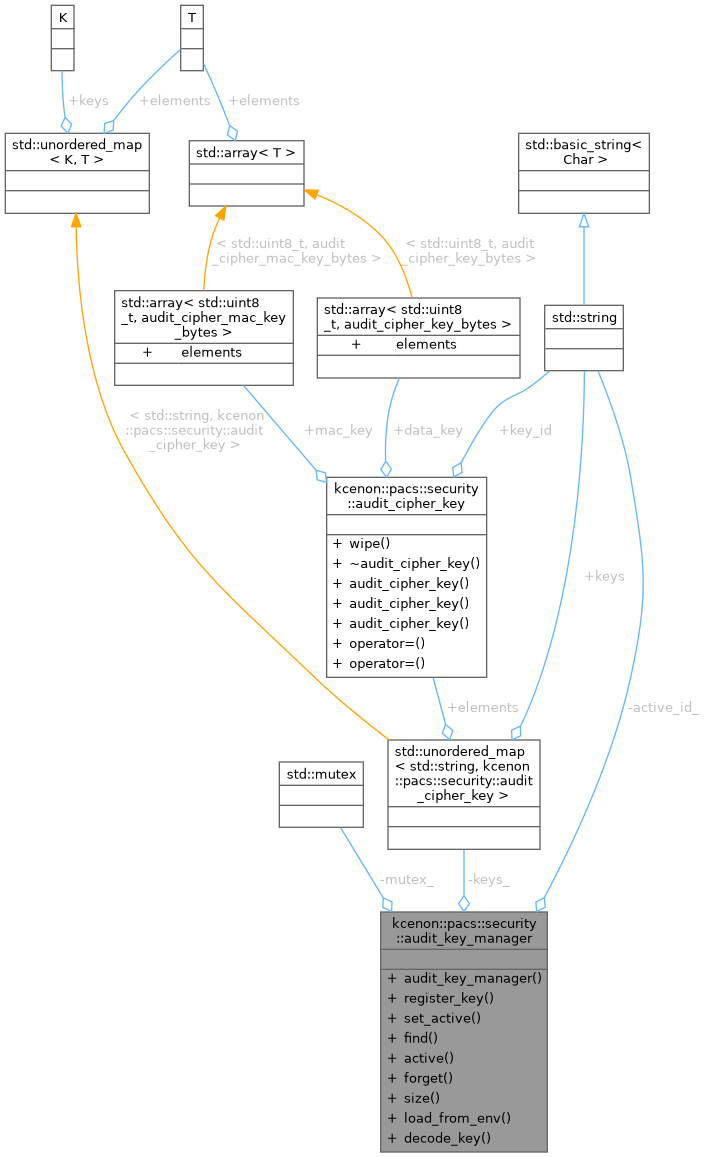
| std::mutex | mutex_ |
| std::unordered_map< std::string, audit_cipher_key > | keys_ |
| std::string | active_id_ |
Detailed Description
Holds the active encryption key and any retired keys for decryption of historical records.
A single "active" key is used for all new writes. Any number of additional keys (including the former active key) may be registered so that previously-written records remain verifiable after rotation.
Thread-safety: all public operations are internally synchronised.
Key sourcing: in production, populate via load_from_env() which reads PACS_AUDIT_LOG_ACTIVE_KEY_ID plus PACS_AUDIT_LOG_KEY_<id> and PACS_AUDIT_LOG_MAC_<id> (both hex- or base64-encoded). NEVER hard-code keys in source. Rotation procedure: provision a new <id>, update PACS_AUDIT_LOG_ACTIVE_KEY_ID, keep the previous key registered for as long as historical records are retained.
Definition at line 123 of file audit_log_cipher.h.
Constructor & Destructor Documentation
◆ audit_key_manager()
|
default |
Member Function Documentation
◆ active()
|
nodiscard |
Retrieve the active write key (error if none configured)
Definition at line 202 of file audit_log_cipher.cpp.
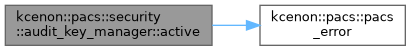
References active_id_, keys_, mutex_, and kcenon::pacs::pacs_error().
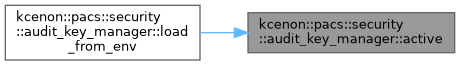
Referenced by load_from_env().
◆ decode_key()
|
staticnodiscard |
Decode a hex or base64 key string into a fixed-size buffer.
Accepts:
- lowercase/uppercase hexadecimal of exactly 2*N characters, or
- base64 (standard alphabet, padding required) of N bytes
- Parameters
-
encoded the encoded string out destination buffer; must be exactly out_sizebytesout_size size of the destination buffer; must equal the key length N
- Returns
- VoidResult success or decode error
Definition at line 229 of file audit_log_cipher.cpp.
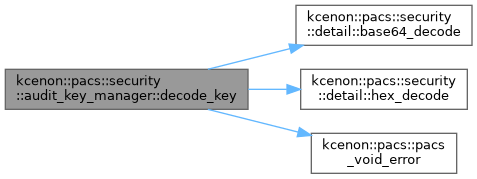
References kcenon::pacs::security::detail::base64_decode(), kcenon::pacs::security::detail::hex_decode(), out, and kcenon::pacs::pacs_void_error().
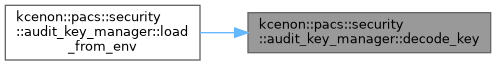
Referenced by load_from_env().
◆ find()
|
nodiscard |
Look up a key by identifier (returns nullptr if unknown)
Definition at line 195 of file audit_log_cipher.cpp.
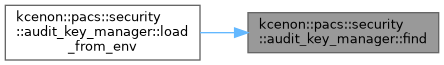
Referenced by load_from_env().
◆ forget()
| void kcenon::pacs::security::audit_key_manager::forget | ( | const std::string & | key_id | ) |
Drop a key by id (does nothing if it was not registered)
Definition at line 218 of file audit_log_cipher.cpp.
References active_id_, keys_, and mutex_.
◆ load_from_env()
|
nodiscard |
Load keys from environment variables.
Reads:
PACS_AUDIT_LOG_ACTIVE_KEY_ID— the active write key idPACS_AUDIT_LOG_KEYS— comma-separated list of ids to load (optional; defaults to the active id only)PACS_AUDIT_LOG_KEY_<id>— 32-byte data key, hex or base64PACS_AUDIT_LOG_MAC_<id>— 32-byte MAC key, hex or base64
- Returns
- VoidResult reporting the first configuration error, if any
Definition at line 290 of file audit_log_cipher.cpp.
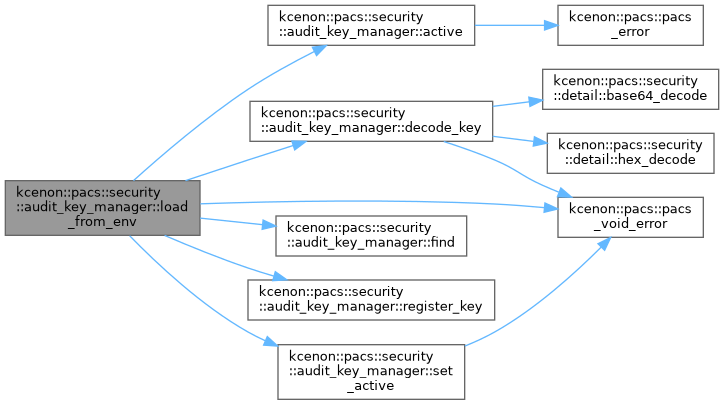
References active(), kcenon::pacs::security::audit_cipher_key::data_key, decode_key(), kcenon::pacs::security::empty, find(), kcenon::pacs::security::audit_cipher_key::key_id, kcenon::pacs::security::list, kcenon::pacs::security::audit_cipher_key::mac_key, kcenon::pacs::pacs_void_error(), register_key(), and set_active().
◆ register_key()
| void kcenon::pacs::security::audit_key_manager::register_key | ( | audit_cipher_key | key | ) |
Register a key (idempotent by key_id; overwrites existing entry)
Definition at line 177 of file audit_log_cipher.cpp.
References active_id_, kcenon::pacs::security::audit_cipher_key::key_id, keys_, and mutex_.
Referenced by load_from_env().
◆ set_active()
|
nodiscard |
Mark a previously-registered key as the active write key.
Definition at line 184 of file audit_log_cipher.cpp.
References active_id_, keys_, mutex_, and kcenon::pacs::pacs_void_error().
Referenced by load_from_env().
◆ size()
|
nodiscard |
Member Data Documentation
◆ active_id_
|
private |
Definition at line 180 of file audit_log_cipher.h.
Referenced by active(), forget(), register_key(), and set_active().
◆ keys_
|
private |
Definition at line 179 of file audit_log_cipher.h.
Referenced by active(), find(), forget(), register_key(), set_active(), and size().
◆ mutex_
|
mutableprivate |
Definition at line 178 of file audit_log_cipher.h.
Referenced by active(), find(), forget(), register_key(), set_active(), and size().
The documentation for this class was generated from the following files:
- include/kcenon/pacs/security/audit_log_cipher.h
- src/security/audit_log_cipher.cpp