Represents a private key for signing operations. More...
#include <certificate.h>
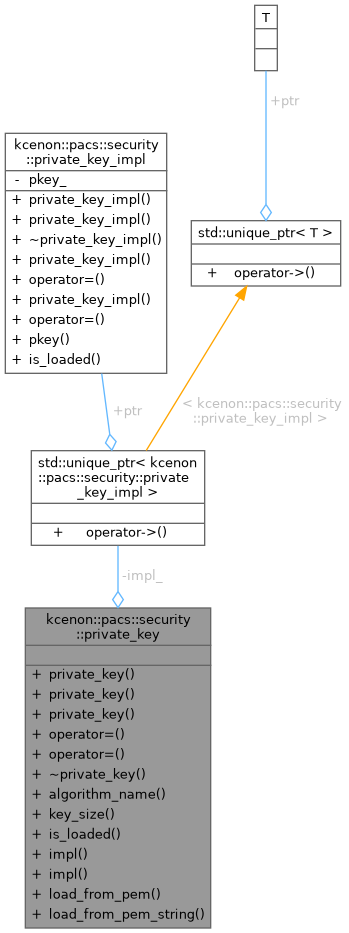
Public Member Functions | |
| private_key () | |
| Default constructor - creates an empty key. | |
| private_key (const private_key &)=delete | |
| Copy constructor (deleted - private keys should not be copied) | |
| private_key (private_key &&other) noexcept | |
| Move constructor. | |
| auto | operator= (const private_key &) -> private_key &=delete |
| Copy assignment (deleted) | |
| auto | operator= (private_key &&other) noexcept -> private_key & |
| Move assignment. | |
| ~private_key () | |
| Destructor - securely erases key material. | |
| auto | algorithm_name () const -> std::string |
| Get the algorithm name. | |
| auto | key_size () const -> int |
| Get the key size in bits. | |
| auto | is_loaded () const noexcept -> bool |
| Check if key is loaded. | |
| auto | impl () const noexcept -> const private_key_impl * |
| Get internal implementation (for internal use only) | |
| auto | impl () noexcept -> private_key_impl * |
Static Public Member Functions | |
| static auto | load_from_pem (std::string_view path, std::string_view password="") -> kcenon::common::Result< private_key > |
| Load private key from PEM file. | |
| static auto | load_from_pem_string (std::string_view pem_data, std::string_view password="") -> kcenon::common::Result< private_key > |
| Load private key from PEM string. | |
Private Attributes | |
| std::unique_ptr< private_key_impl > | impl_ |
Detailed Description
Represents a private key for signing operations.
This class wraps a private key (RSA or EC) and provides methods to load and use the key for digital signature creation.
Thread Safety: This class is thread-safe for read operations.
- Example:
- if (key_result.is_ok()) {auto& key = key_result.value();std::cout << "Key type: " << key.algorithm_name() << "\n";std::cout << "Key size: " << key.key_size() << " bits\n";}static auto load_from_pem(std::string_view path, std::string_view password="") -> kcenon::common::Result< private_key >Load private key from PEM file.Definition certificate.cpp:570
Definition at line 239 of file certificate.h.
Constructor & Destructor Documentation
◆ private_key() [1/3]
| kcenon::pacs::security::private_key::private_key | ( | ) |
Default constructor - creates an empty key.
Definition at line 562 of file certificate.cpp.
◆ private_key() [2/3]
|
delete |
Copy constructor (deleted - private keys should not be copied)
◆ private_key() [3/3]
|
defaultnoexcept |
Move constructor.
◆ ~private_key()
|
default |
Destructor - securely erases key material.
Member Function Documentation
◆ algorithm_name()
|
nodiscard |
Get the algorithm name.
- Returns
- Algorithm name (e.g., "RSA", "EC")
Definition at line 610 of file certificate.cpp.
References impl_.
◆ impl() [1/2]
|
nodiscardnoexcept |
Get internal implementation (for internal use only)
Definition at line 645 of file certificate.cpp.
References impl_.
◆ impl() [2/2]
|
nodiscardnoexcept |
Definition at line 649 of file certificate.cpp.
References impl_.
◆ is_loaded()
|
nodiscardnoexcept |
Check if key is loaded.
- Returns
- true if key data is loaded
Definition at line 641 of file certificate.cpp.
References impl_.
◆ key_size()
|
nodiscard |
Get the key size in bits.
- Returns
- Key size (e.g., 2048, 4096 for RSA; 256, 384 for EC)
Definition at line 633 of file certificate.cpp.
References impl_.
◆ load_from_pem()
|
staticnodiscard |
Load private key from PEM file.
- Parameters
-
path Path to PEM-encoded private key file password Optional password for encrypted keys (empty for unencrypted)
- Returns
- Result containing private key or error
Definition at line 570 of file certificate.cpp.
◆ load_from_pem_string()
|
staticnodiscard |
Load private key from PEM string.
- Parameters
-
pem_data PEM-encoded private key data password Optional password for encrypted keys
- Returns
- Result containing private key or error
Definition at line 583 of file certificate.cpp.
References impl_.
◆ operator=() [1/2]
|
delete |
Copy assignment (deleted)
◆ operator=() [2/2]
|
defaultnoexcept |
Move assignment.
Member Data Documentation
◆ impl_
|
private |
Definition at line 330 of file certificate.h.
Referenced by algorithm_name(), impl(), impl(), is_loaded(), key_size(), and load_from_pem_string().
The documentation for this class was generated from the following files:
- include/kcenon/pacs/security/certificate.h
- src/security/certificate.cpp