ITI-41 Document Source actor. More...
#include <document_source.h>
Classes | |
| class | impl |
Public Member Functions | |
| document_source (http_options opts, signing_material signing) | |
| Construct an ITI-41 Document Source bound to an endpoint and a signing credential. | |
| document_source (document_source &&) noexcept | |
| document_source & | operator= (document_source &&) noexcept |
| document_source (const document_source &)=delete | |
| document_source & | operator= (const document_source &)=delete |
| ~document_source () | |
| kcenon::common::Result< submit_response > | submit (const submission_set &s) |
| Submit an XDS.b submission set. | |
| void | set_audit_sink (std::shared_ptr< kcenon::pacs::security::xds_audit_sink > sink) |
| Install an ATNA audit sink. | |
Private Attributes | |
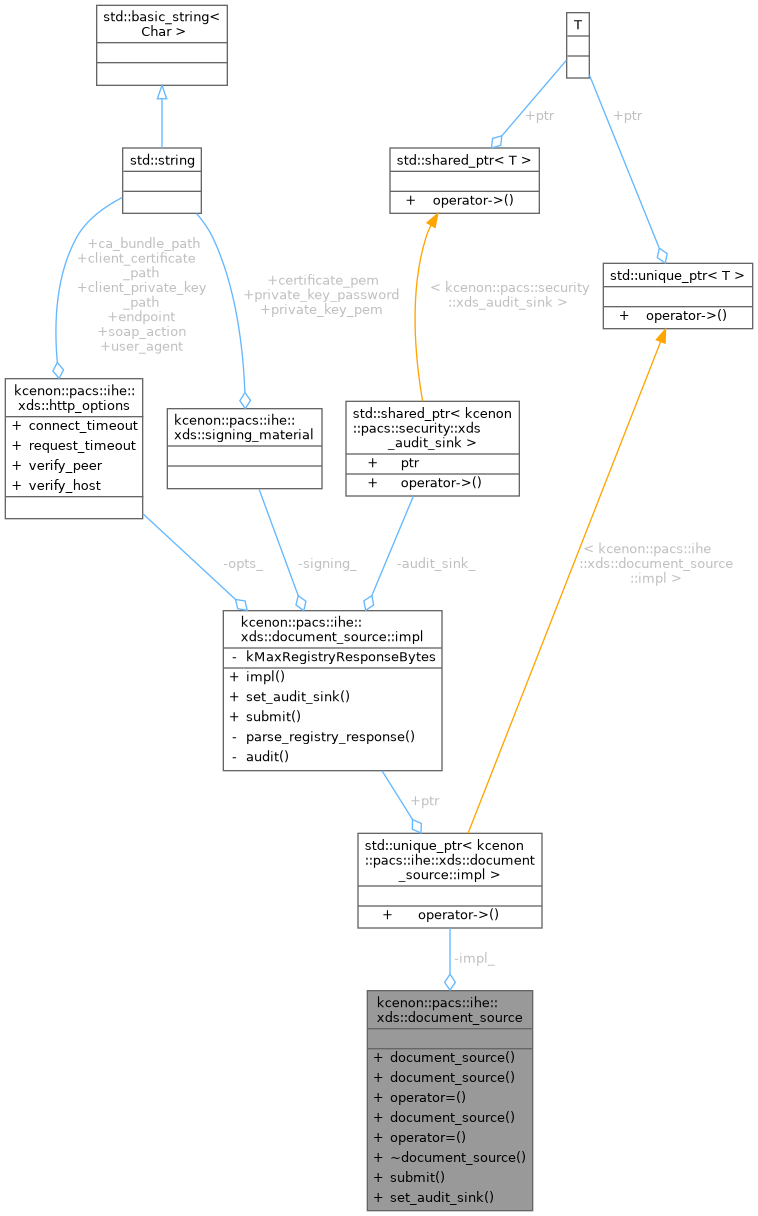
| std::unique_ptr< impl > | impl_ |
Detailed Description
ITI-41 Document Source actor.
The instance is bound to one endpoint and one signing credential. To submit to different registries or sign with different certificates, instantiate multiple document_source objects.
Thread-safety: a single instance is safe to destroy but submit() is NOT reentrant - callers must serialize submit calls per instance, or create one instance per worker thread. libcurl handles are owned by the impl and may not be shared between threads.
Definition at line 84 of file document_source.h.
Constructor & Destructor Documentation
◆ document_source() [1/3]
| kcenon::pacs::ihe::xds::document_source::document_source | ( | http_options | opts, |
| signing_material | signing ) |
Construct an ITI-41 Document Source bound to an endpoint and a signing credential.
Signing material is copied into the instance; the caller may then zeroize the original buffer. The constructor never throws - any material validation failure is deferred to submit() and surfaces as a typed error_code.
Definition at line 219 of file document_source.cpp.
◆ document_source() [2/3]
|
defaultnoexcept |
◆ document_source() [3/3]
|
delete |
◆ ~document_source()
|
default |
Member Function Documentation
◆ operator=() [1/2]
|
delete |
◆ operator=() [2/2]
|
defaultnoexcept |
◆ set_audit_sink()
| void kcenon::pacs::ihe::xds::document_source::set_audit_sink | ( | std::shared_ptr< kcenon::pacs::security::xds_audit_sink > | sink | ) |
Install an ATNA audit sink.
When set, submit() emits exactly one audit event per invocation - success or failure - carrying the submission_set unique id, patient id, registry endpoint, and the outcome code. A null sink (the default) disables emission. The sink is shared ownership so the same sink instance can be installed on multiple actors feeding a single auditor.
- See also
- kcenon::pacs::security::xds_audit_sink
- Issue #1131
Definition at line 232 of file document_source.cpp.
References impl_, and kcenon::pacs::ihe::xds::document_source::impl::set_audit_sink().
◆ submit()
| kcenon::common::Result< submit_response > kcenon::pacs::ihe::xds::document_source::submit | ( | const submission_set & | s | ) |
Submit an XDS.b submission set.
Sequence: validate metadata -> build ebRIM SubmitObjectsRequest SOAP envelope -> WS-Security sign Timestamp+Body -> wrap body parts in multipart/related MTOM payload -> POST to configured endpoint over HTTPS -> parse RegistryResponse.
All failure modes surface as typed error_code values; the function never throws across the API boundary. On success, the returned submit_response echoes the registry's Success status and the submission set unique id.
Definition at line 227 of file document_source.cpp.
References submit().
Referenced by submit().
Member Data Documentation
◆ impl_
|
private |
Definition at line 138 of file document_source.h.
Referenced by set_audit_sink().
The documentation for this class was generated from the following files:
- include/kcenon/pacs/ihe/xds/document_source.h
- src/ihe/xds/document_source.cpp