Signing material for WS-Security XML-DSig. More...
#include <document_source.h>
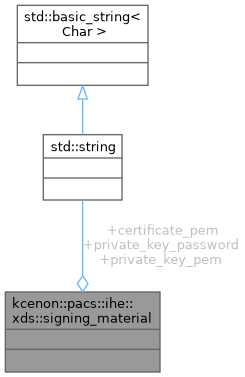
Public Attributes | |
| std::string | certificate_pem |
| std::string | private_key_pem |
| std::string | private_key_password |
Detailed Description
Signing material for WS-Security XML-DSig.
certificate_pem is the X.509 signer certificate in PEM form. The Document Source embeds its DER-encoded form as a BinarySecurityToken.
private_key_pem is the matching RSA or EC private key in PEM form. If password-protected, the PEM passphrase dialog is bypassed by the provided password field.
PEM strings are loaded directly rather than using the security classes so callers can source them from an HSM-backed buffer that never hits disk. Both the certificate and key are validated lazily on the first submit() call; malformed material produces a typed error_code value rather than a constructor exception.
Definition at line 66 of file document_source.h.
Member Data Documentation
◆ certificate_pem
| std::string kcenon::pacs::ihe::xds::signing_material::certificate_pem |
Definition at line 67 of file document_source.h.
Referenced by kcenon::pacs::ihe::xds::registry_query::impl::execute(), kcenon::pacs::ihe::xds::document_consumer::impl::retrieve(), and kcenon::pacs::ihe::xds::document_source::impl::submit().
◆ private_key_password
| std::string kcenon::pacs::ihe::xds::signing_material::private_key_password |
Definition at line 69 of file document_source.h.
Referenced by kcenon::pacs::ihe::xds::registry_query::impl::execute(), kcenon::pacs::ihe::xds::document_consumer::impl::retrieve(), and kcenon::pacs::ihe::xds::document_source::impl::submit().
◆ private_key_pem
| std::string kcenon::pacs::ihe::xds::signing_material::private_key_pem |
Definition at line 68 of file document_source.h.
Referenced by kcenon::pacs::ihe::xds::registry_query::impl::execute(), kcenon::pacs::ihe::xds::document_consumer::impl::retrieve(), and kcenon::pacs::ihe::xds::document_source::impl::submit().
The documentation for this struct was generated from the following file:
- include/kcenon/pacs/ihe/xds/document_source.h
