Loading...
Searching...
No Matches
wss_signer.h File Reference
WS-Security XML-DSig signer backed by OpenSSL EVP_DigestSign. More...
#include <kcenon/common/patterns/result.h>#include <kcenon/pacs/ihe/xds/errors.h>#include <cstdint>#include <string>#include <string_view>#include <vector>
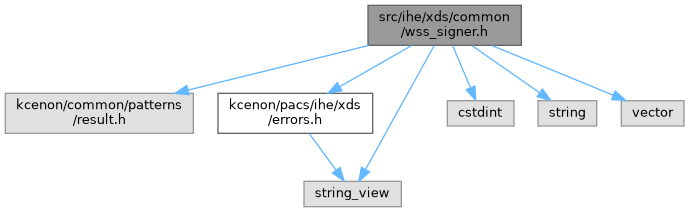
Include dependency graph for wss_signer.h:
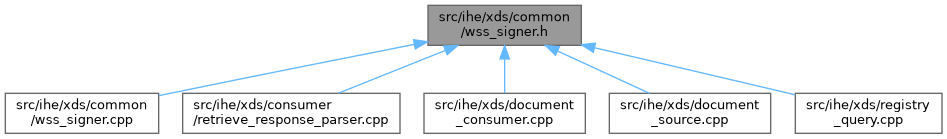
This graph shows which files directly or indirectly include this file:
Go to the source code of this file.
Namespaces | |
| namespace | kcenon |
| namespace | kcenon::pacs |
| namespace | kcenon::pacs::ihe |
| namespace | kcenon::pacs::ihe::xds |
| namespace | kcenon::pacs::ihe::xds::detail |
Functions | |
| kcenon::common::Result< bool > | kcenon::pacs::ihe::xds::detail::sign_envelope (built_envelope &env, std::string_view cert_pem, std::string_view key_pem, std::string_view key_password) |
Sign the body + timestamp of env in place. | |
| kcenon::common::Result< bool > | kcenon::pacs::ihe::xds::detail::verify_envelope_integrity (std::string_view signed_xml) |
| Verify the structural integrity of a previously signed envelope against the certificate embedded in its own BinarySecurityToken. | |
| std::vector< std::uint8_t > | kcenon::pacs::ihe::xds::detail::base64_decode_bytes (std::string_view b64) |
Base64-decode b64 using the same BIO-backed decoder the signer and verifier use internally. | |
Detailed Description
WS-Security XML-DSig signer backed by OpenSSL EVP_DigestSign.
Signs the <soap:Body> and <wsu:Timestamp> of a previously constructed envelope and injects <ds:Signature> into the <wsse:Security> header. The resulting XML is ready for transmission.
Canonicalization: exc-c14n (http://www.w3.org/2001/10/xml-exc-c14n#). Signature method: RSA-SHA256. KeyInfo points to the BinarySecurityToken that already exists in the envelope header.
This is an internal header.
Definition in file wss_signer.h.
