OpenSSL-backed WS-Security XML-DSig signer. More...
#include "wss_signer.h"#include "soap_envelope.h"#include <openssl/bio.h>#include <openssl/err.h>#include <openssl/evp.h>#include <openssl/pem.h>#include <openssl/sha.h>#include <openssl/x509.h>#include <pugixml.hpp>#include <cstring>#include <cstdio>#include <memory>#include <string>#include <vector>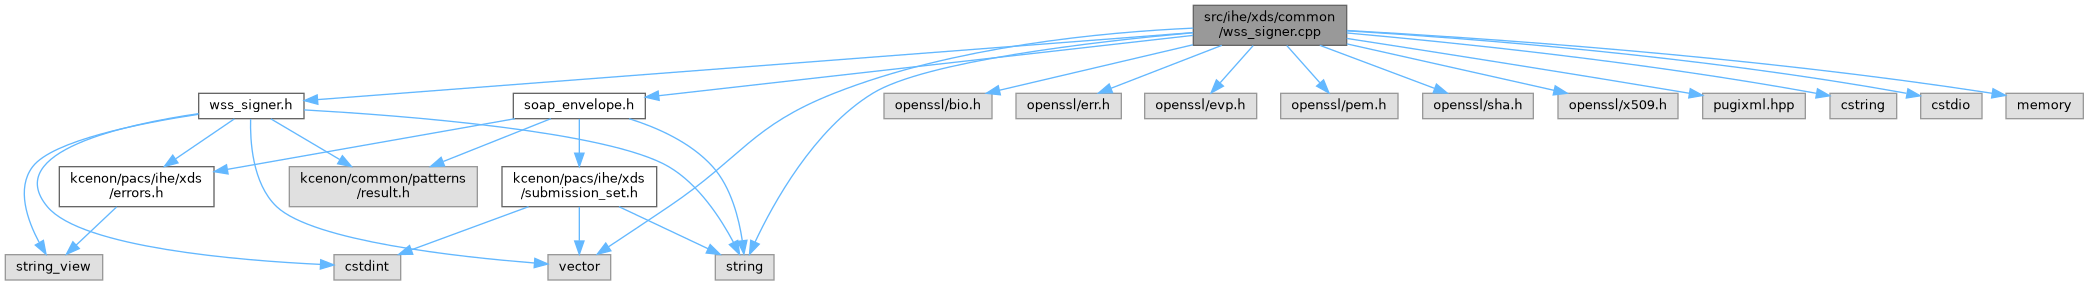
Go to the source code of this file.
Namespaces | |
| namespace | kcenon |
| namespace | kcenon::pacs |
| namespace | kcenon::pacs::ihe |
| namespace | kcenon::pacs::ihe::xds |
| namespace | kcenon::pacs::ihe::xds::detail |
Functions | |
| kcenon::common::Result< bool > | kcenon::pacs::ihe::xds::detail::sign_envelope (built_envelope &env, std::string_view cert_pem, std::string_view key_pem, std::string_view key_password) |
Sign the body + timestamp of env in place. | |
| kcenon::common::Result< bool > | kcenon::pacs::ihe::xds::detail::verify_envelope_integrity (std::string_view signed_xml) |
| Verify the structural integrity of a previously signed envelope against the certificate embedded in its own BinarySecurityToken. | |
| std::vector< std::uint8_t > | kcenon::pacs::ihe::xds::detail::base64_decode_bytes (std::string_view b64) |
Base64-decode b64 using the same BIO-backed decoder the signer and verifier use internally. | |
Detailed Description
OpenSSL-backed WS-Security XML-DSig signer.
Canonicalization policy
This signer does NOT implement Exclusive XML Canonicalization (http://www.w3.org/2001/10/xml-exc-c14n#). It serializes referenced nodes with pugixml's format_raw, which produces deterministic UTF-8 XML with no whitespace perturbation. Because the envelope built by soap_envelope.cpp declares every namespace on <soap:Envelope> at build time, every descendant inherits the same prefix bindings, so the byte stream is stable under our own verifier. It is NOT interoperable with a strict exc-c14n implementation (IHE Gazelle, .NET WIF, Apache CXF), which would require namespace rewriting and attribute ordering.
The advertised CanonicalizationMethod / Transform Algorithm URIs in the emitted <ds:Signature> are therefore the project-local identifier
urn:kcenon:xds:c14n:pugixml-format-raw-v1
NOT the exc-c14n URI. This is deliberate: advertising exc-c14n while emitting something else would silently produce signatures that look valid to our own test (EVP_DigestVerify over the same serializer) but fail in any third-party verifier. The project-local URI makes non-interoperable callers fail loudly at Algorithm check instead.
Full exc-c14n + Apache CXF / Gazelle round-trip verification is tracked as a follow-up issue and must land before production use against a real XDS.b registry.
Addresses review finding MAJOR-2 (Option A - honest URI).
Definition in file wss_signer.cpp.
Variable Documentation
◆ match
| pugi::xml_node match |
Definition at line 393 of file wss_signer.cpp.
Referenced by kcenon::pacs::ihe::xds::detail::parse_retrieve_response(), and kcenon::pacs::client::sync_manager::impl::query_remote_studies().
◆ needle
| std::string needle |
Definition at line 392 of file wss_signer.cpp.
◆ out
| std::string out |
Definition at line 191 of file wss_signer.cpp.
